---
title: "Deploying Okta Desktop Password Sync and Platform Single Sign-On"
slug: "deploying-okta-desktop-password-sync-and-platform-single-sign-on"
updated: 2025-08-22T19:02:53Z
published: 2025-08-22T19:02:53Z
canonical: "support.kandji.io/deploying-okta-desktop-password-sync-and-platform-single-sign-on"
---
> ## Documentation Index
> Fetch the complete documentation index at: https://support.kandji.io/kb/llms.txt
> Use this file to discover all available pages before exploring further.
# Deploying Okta Desktop Password Sync and Platform Single Sign-On
> [!WARNING]
> Okta Desktop Password Sync is currently in Okta "Early Access" release. See Okta's resource: [Manage Early Access and Beta](https://help.okta.com/oie/en-us/content/topics/security/manage-ea-and-beta-features.htm).
### Requirements
#### Okta Requirements
- Your Okta Identity Engine org is available.
- Your macOS computers are running a minimum of macOS Ventura 13.
- Support for Platform SSO 2.0 is available for macOS computers using macOS 14 Sonoma and later. Platform SSO 2.0 allows users to use Desktop Password Sync directly from the macOS login window.
- The Desktop Password Sync application is available for your organization in Okta. If you can't locate the Desktop Password Sync app in the app catalog, contact your Okta account representative.
- The Okta Verify authenticator is set up in your org.
- The Okta Verify app added to your Kandji tenant from Apple Business Manager Apps & Books (See Kandji guide [here](/v1/docs/add-apps-from-apps-and-books-to-kandji)).
#### Additional Requirements
- A plain text editor such as Visual Studio Code, Sublime Text, BBEdit, etc.
- Three mobileconfig files that will be edited and uploaded to Kandji as Custom Profiles.
### FileVault Support for macOS 15+
Okta has new authentication policies available to enforce stronger authentication requirements for macOS 15+. The Desktop Password Sync experience now includes the FileVault interface. You can read more about this in Okta’s [Configure Desktop Password Sync for macOS 15](https://help.okta.com/oie/en-us/content/topics/oda/macos-pw-sync/update-password-sync-for-mac-15.htm#fvnetwork) article.
### Create Device Access SCEP Certificates for macOS 14+
#### Configure a Desktop SCEP Certificate Authority in Okta
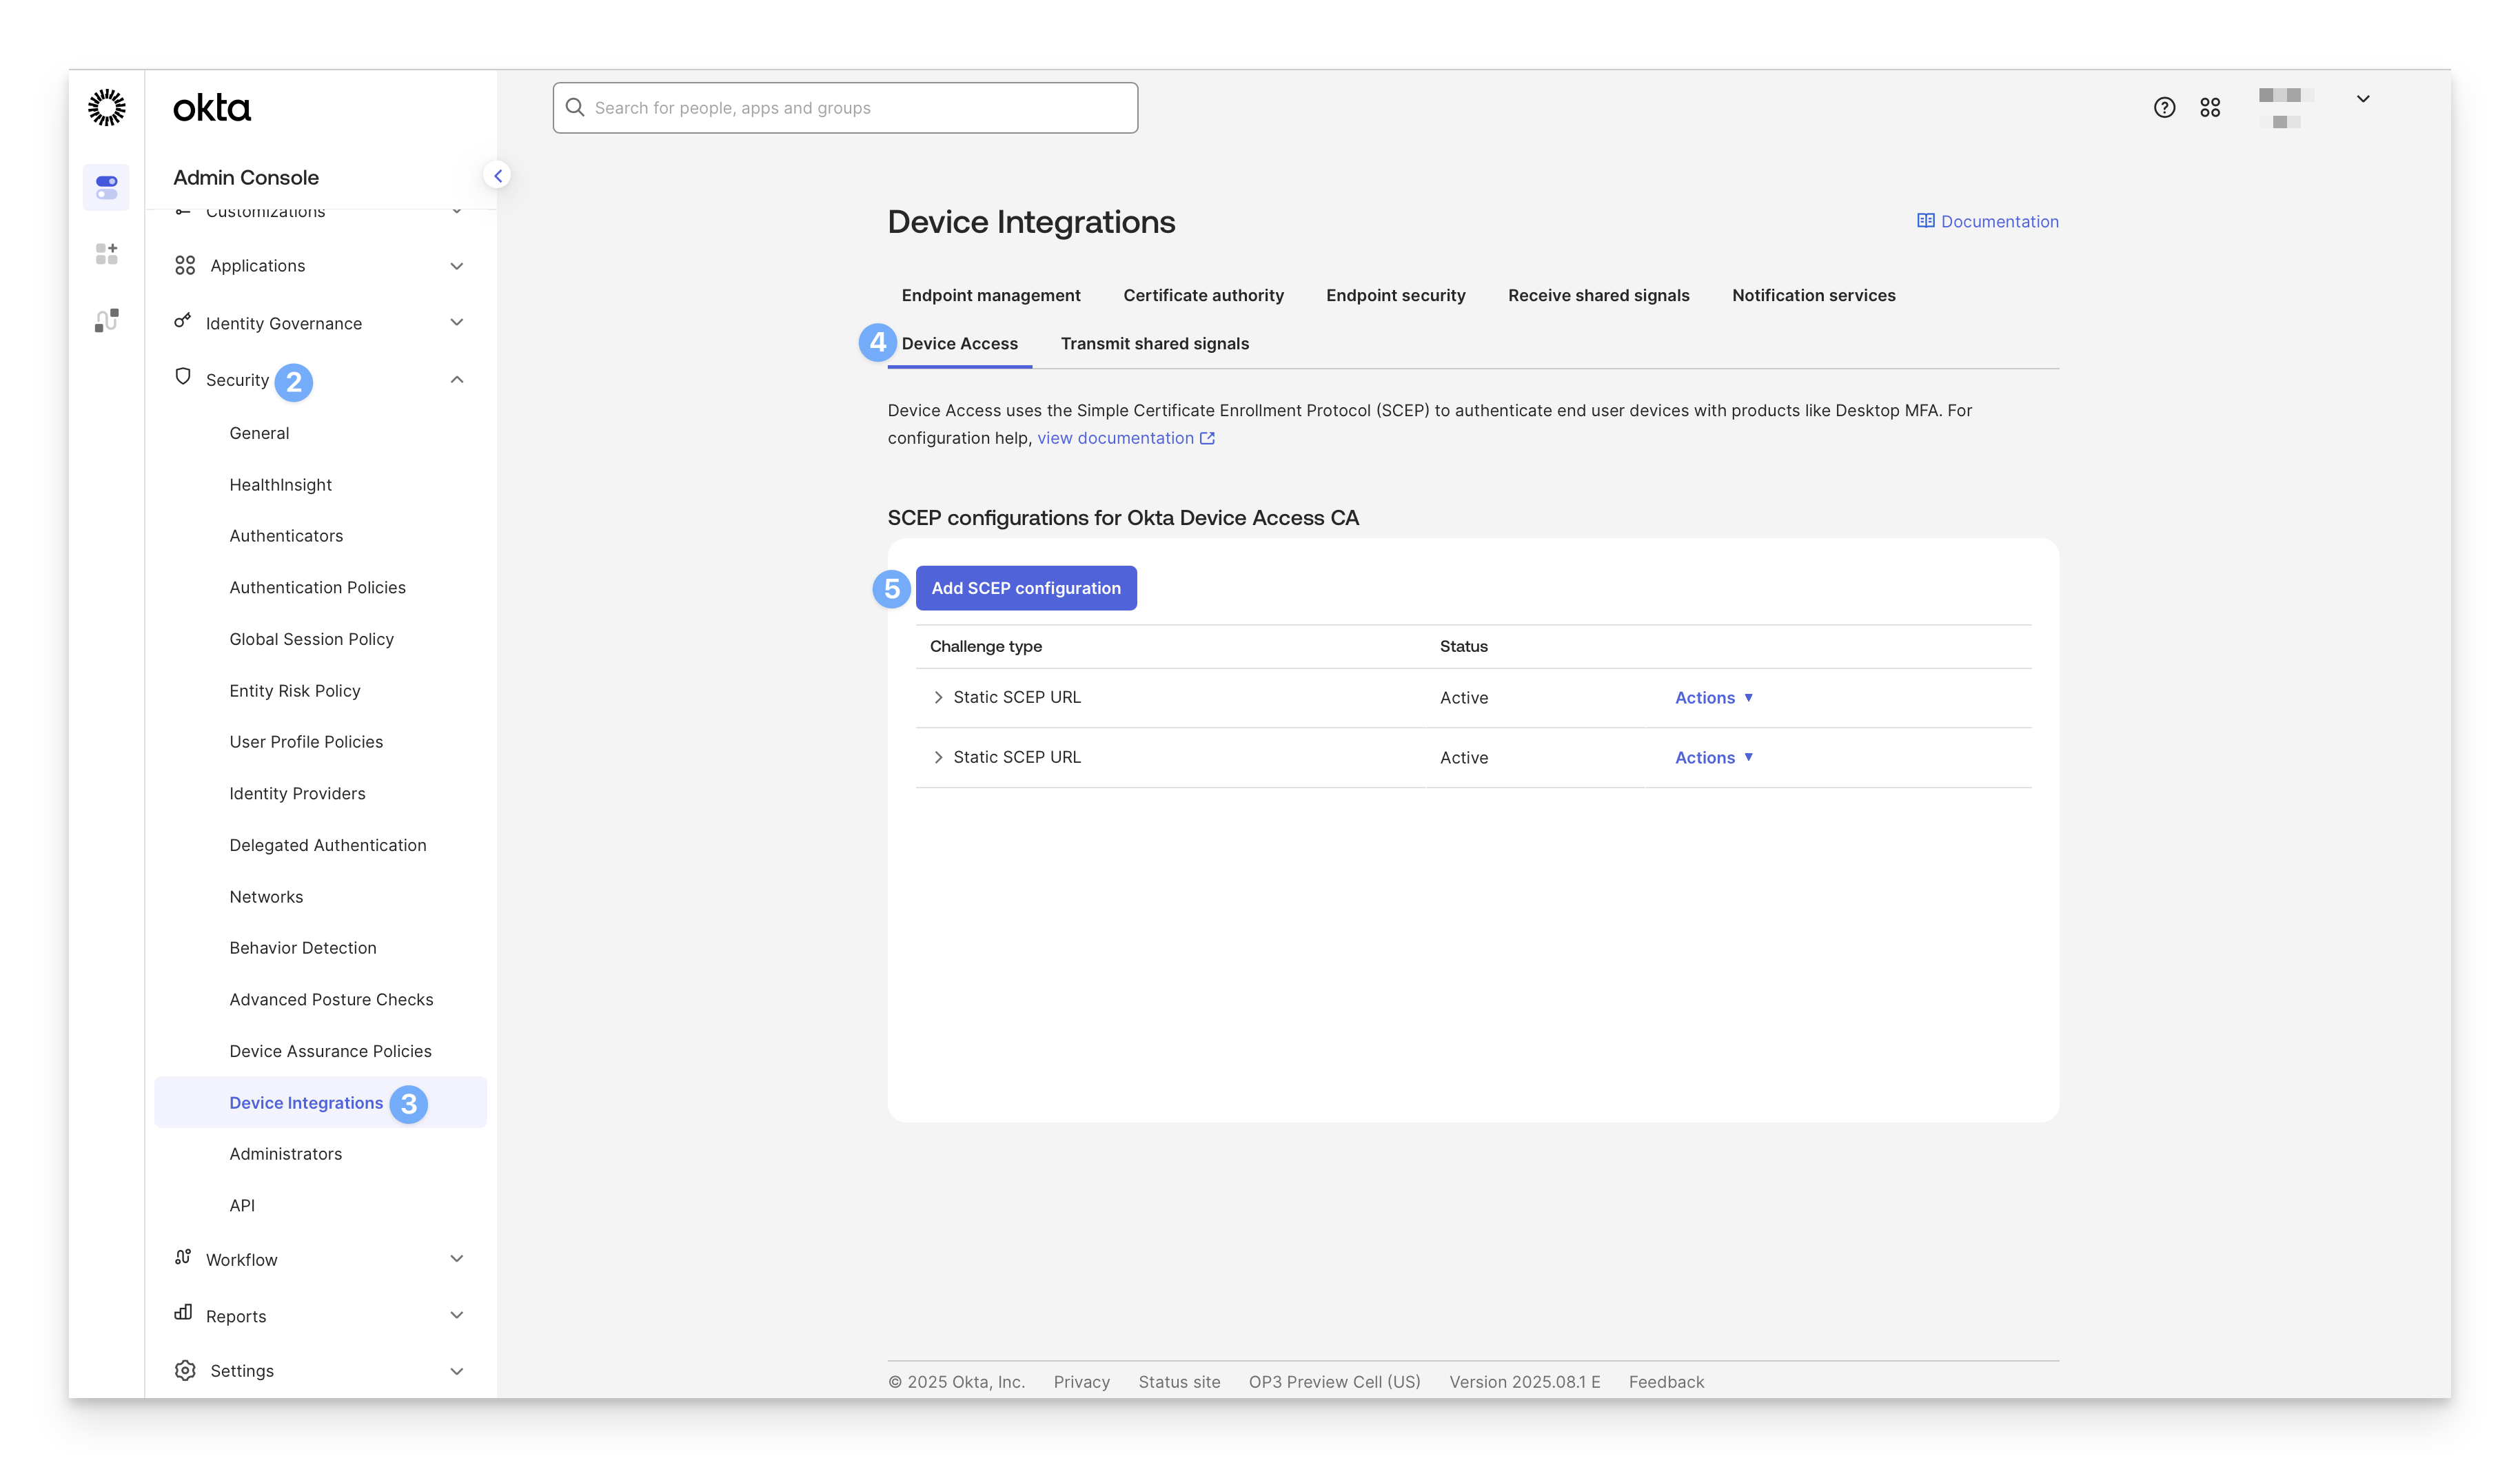
1. Log in to your Okta admin portal.
2. In the left-hand navigation, select **Security**.
3. In the expanded menu, select **Device Integrations**.
4. In the Device Integration pane, select **Device Access**.
5. Click **Add SCEP configuration**.
6. Select **Static SCEP URL**.
7. Click **Generate**. 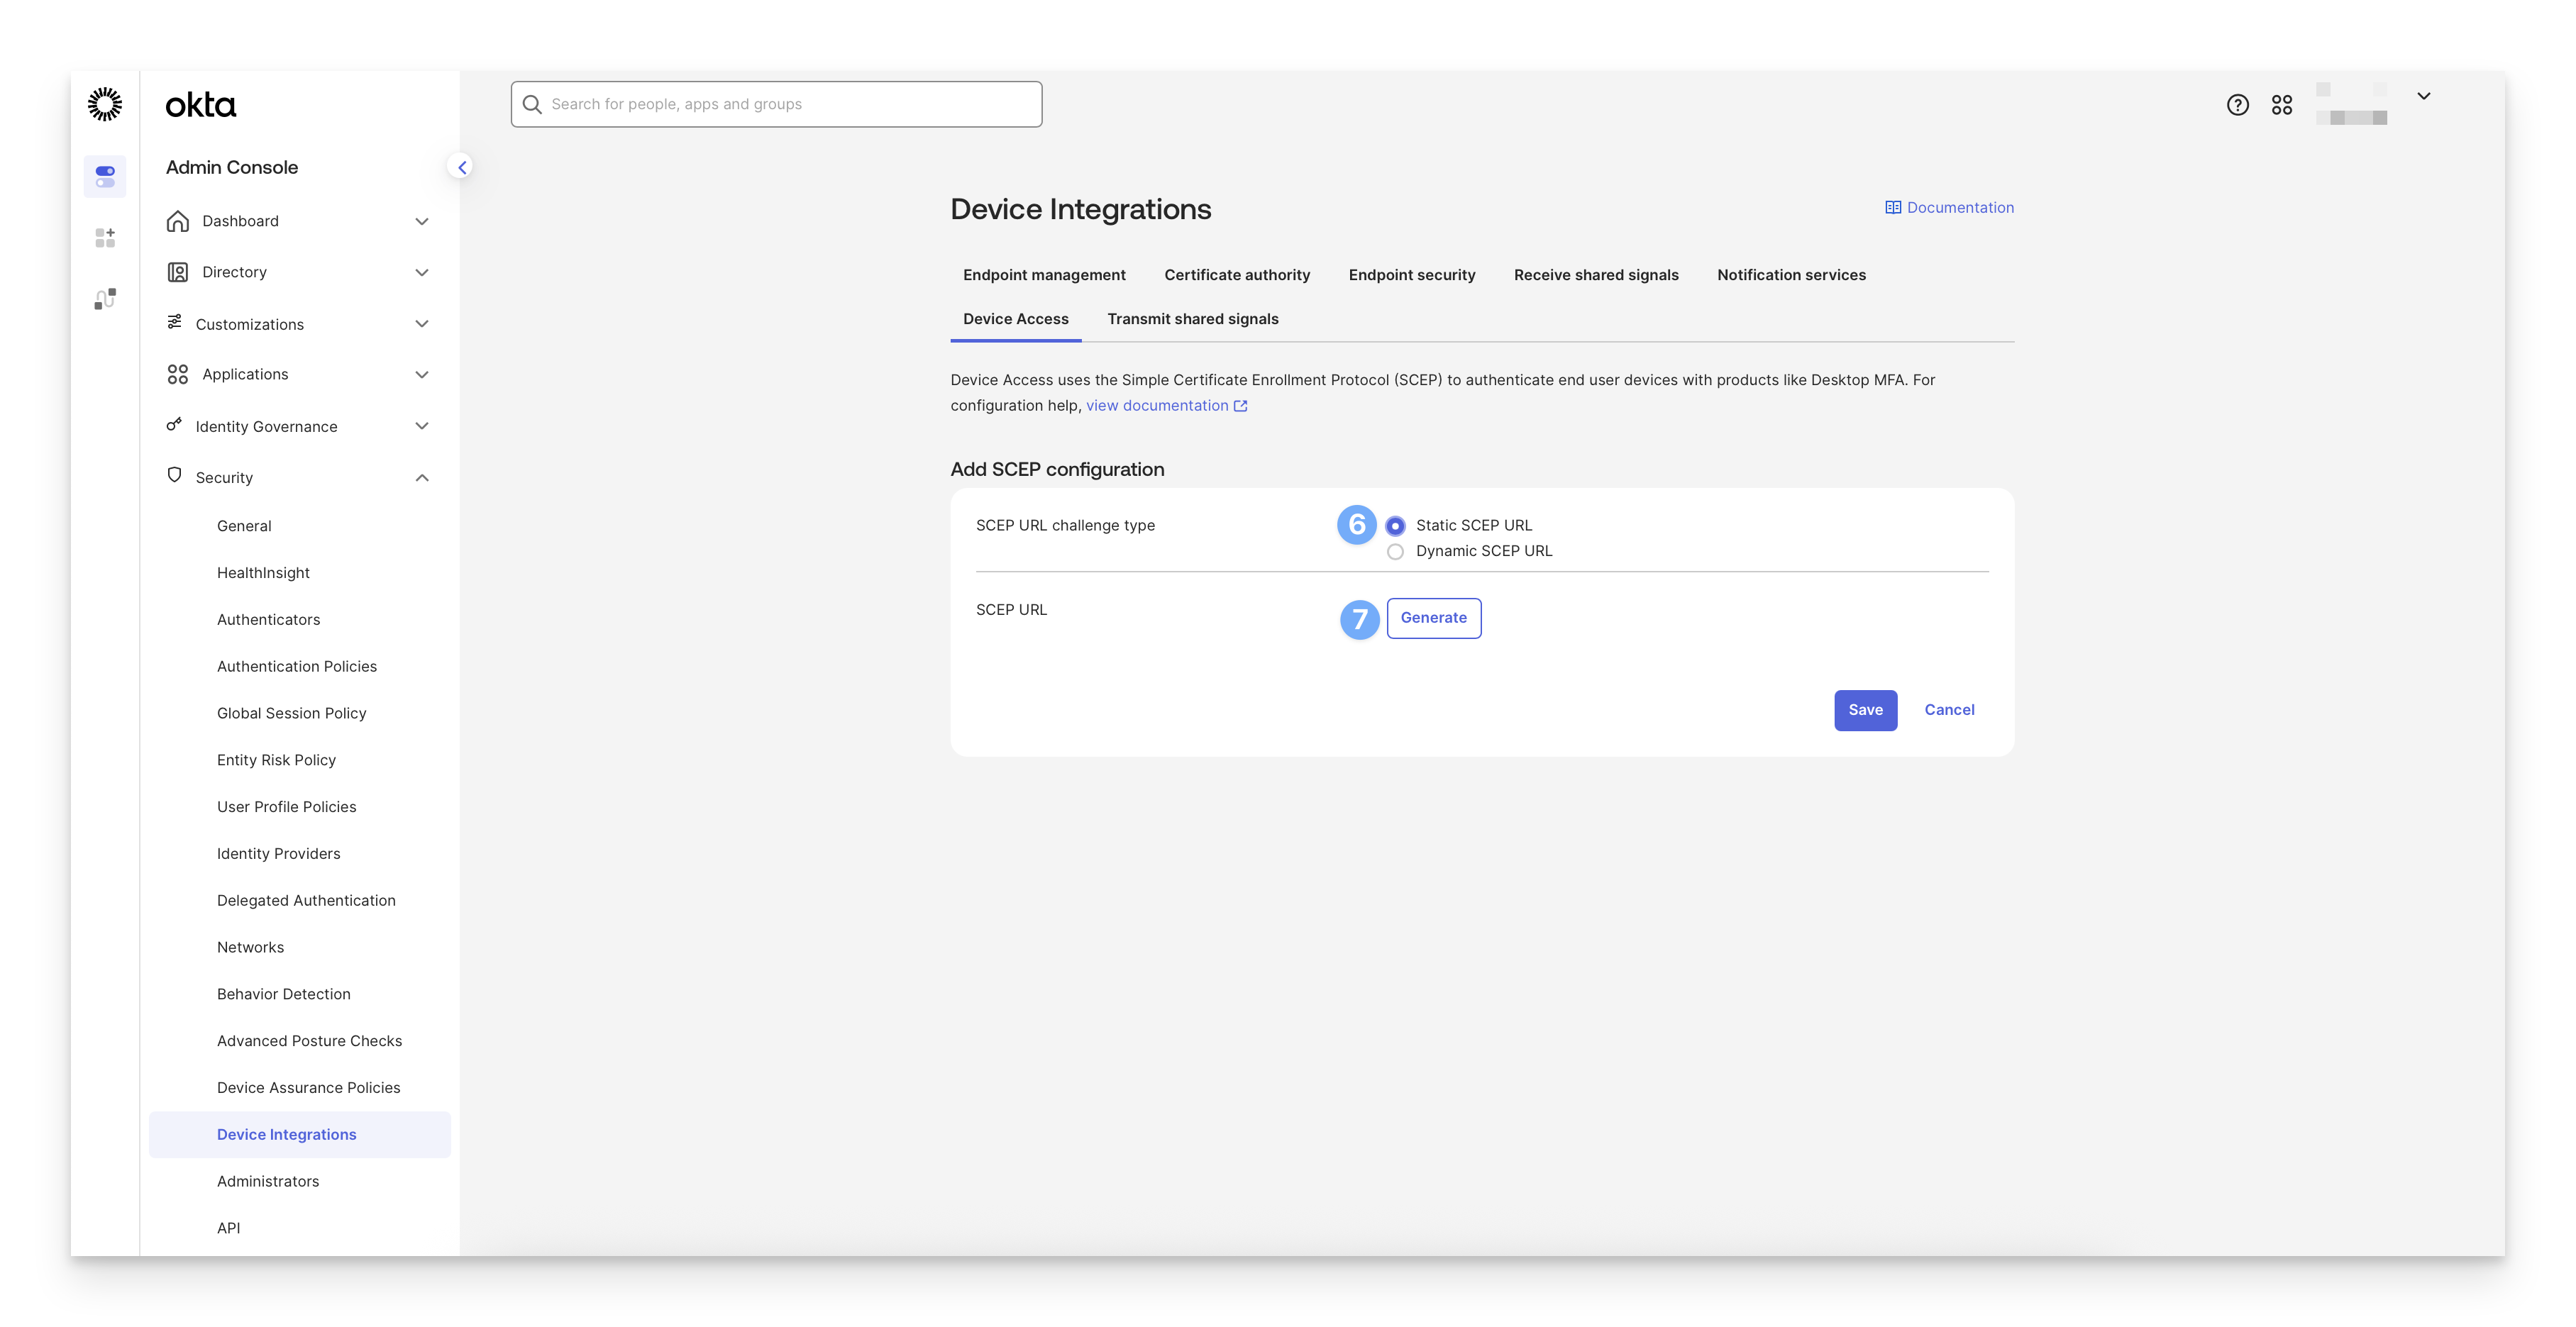
8. Copy the **SCEP URL**.
9. Copy the **Secret key**.
- Make a note of the secret key, as this is the only time you will be able to view it. After this, it will be stored as a hash for your protection. If needed, this key can be rotated.
10. Click **Save**.
1.
- If you need to **Reset the secret key**, you can do so from the **Actions** menu to the right of the integration. 
#### Add the SCEP Payload to Your Kandji Library
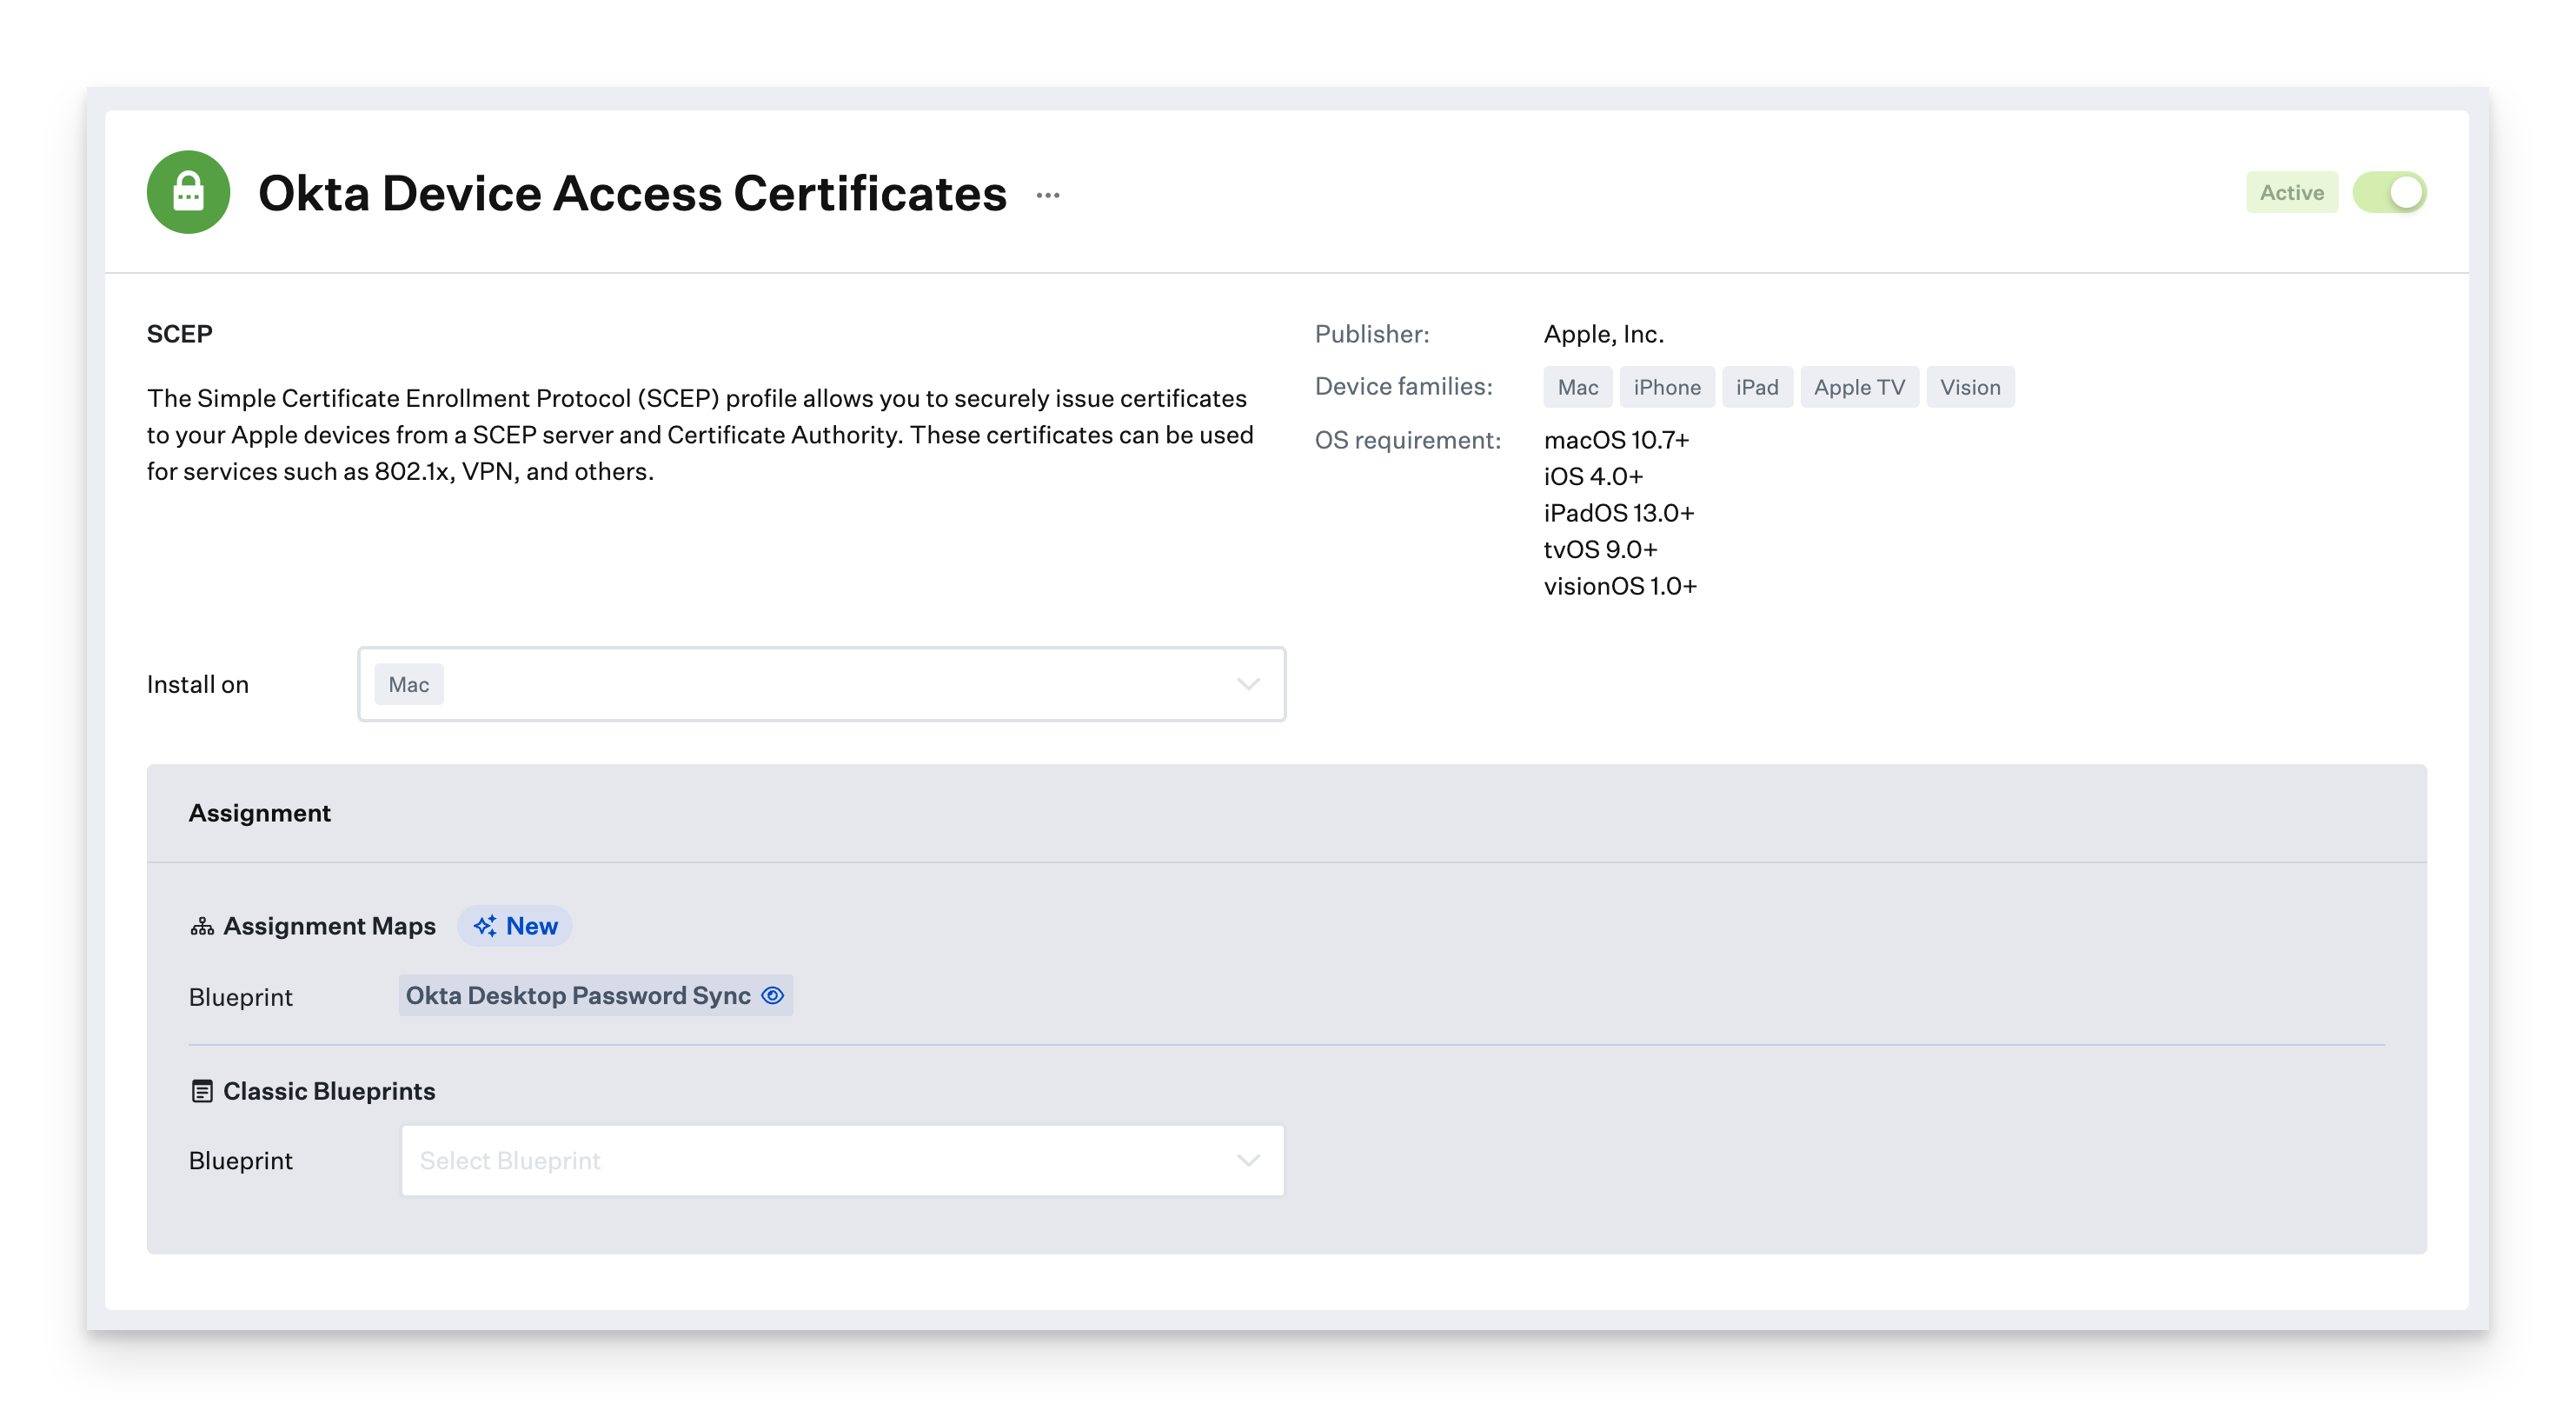
To add this Library Item to your Kandji Library, follow the steps outlined in the [Library Overview](/kb/library-overview) article.
#### Configure the SCEP Certificate Profile
1. Give the profile a name.
2. Assign it to your desired [Blueprints](/v1/docs/getting-started-with-assignment-maps).
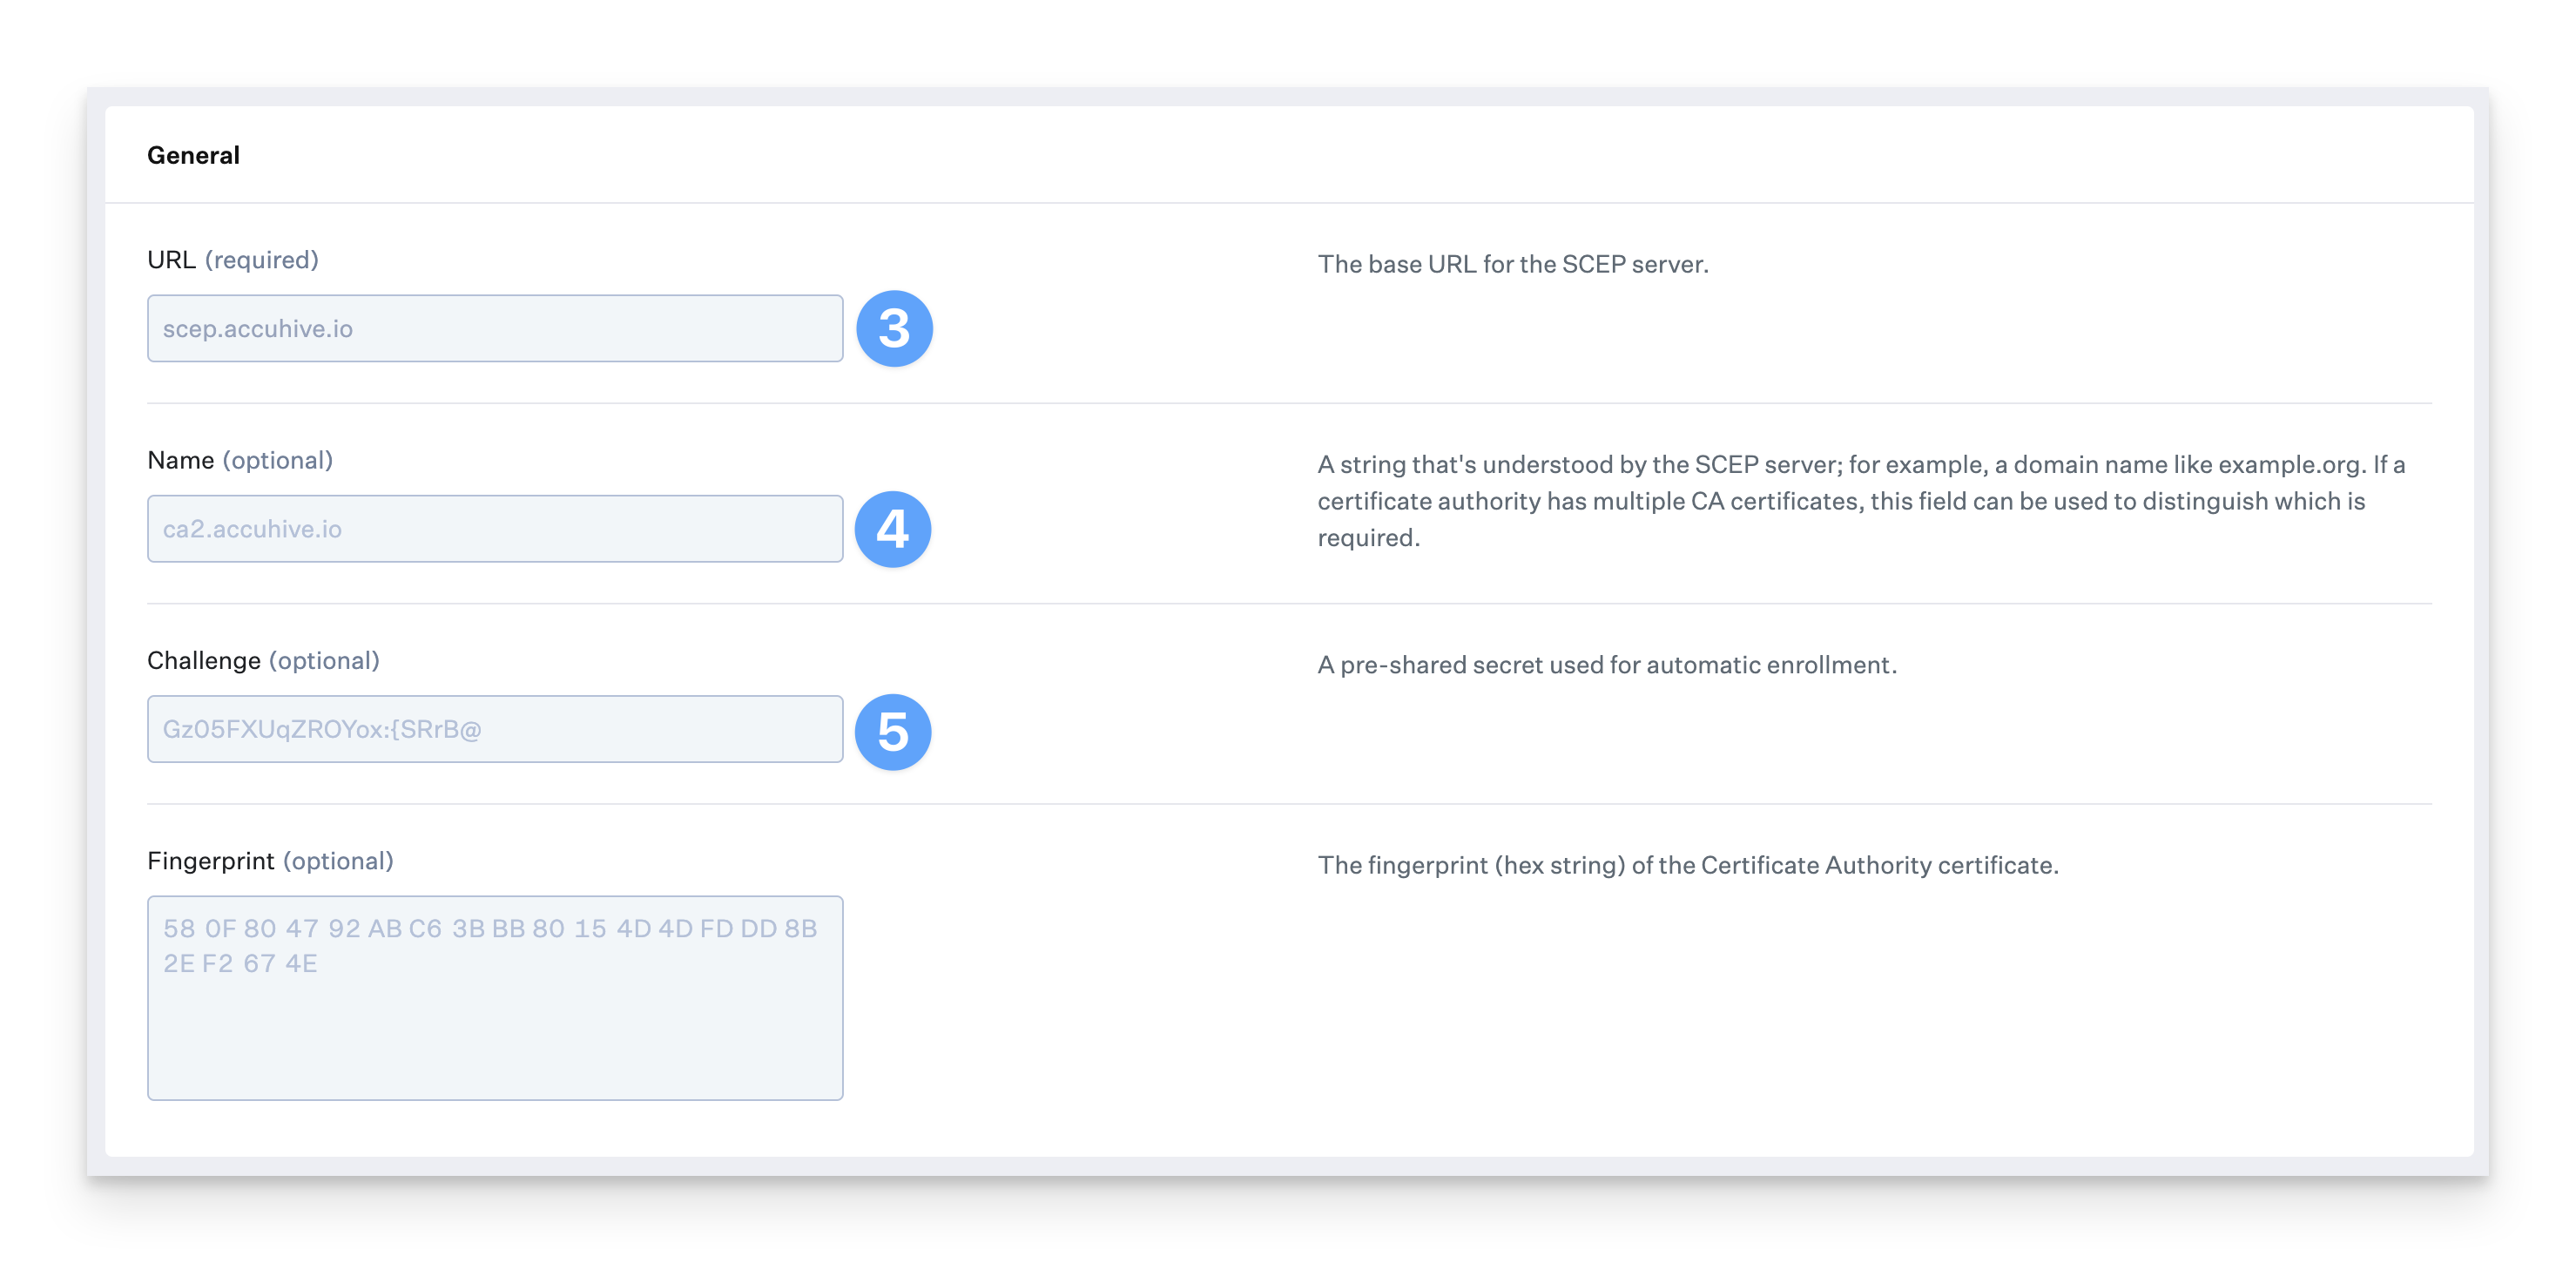
3. In the **URL** field, paste the SCEP server URL you copied earlier.
4. Enter a **Name** (optional).
5. In the **Challenge** field, paste the secret key you copied earlier.
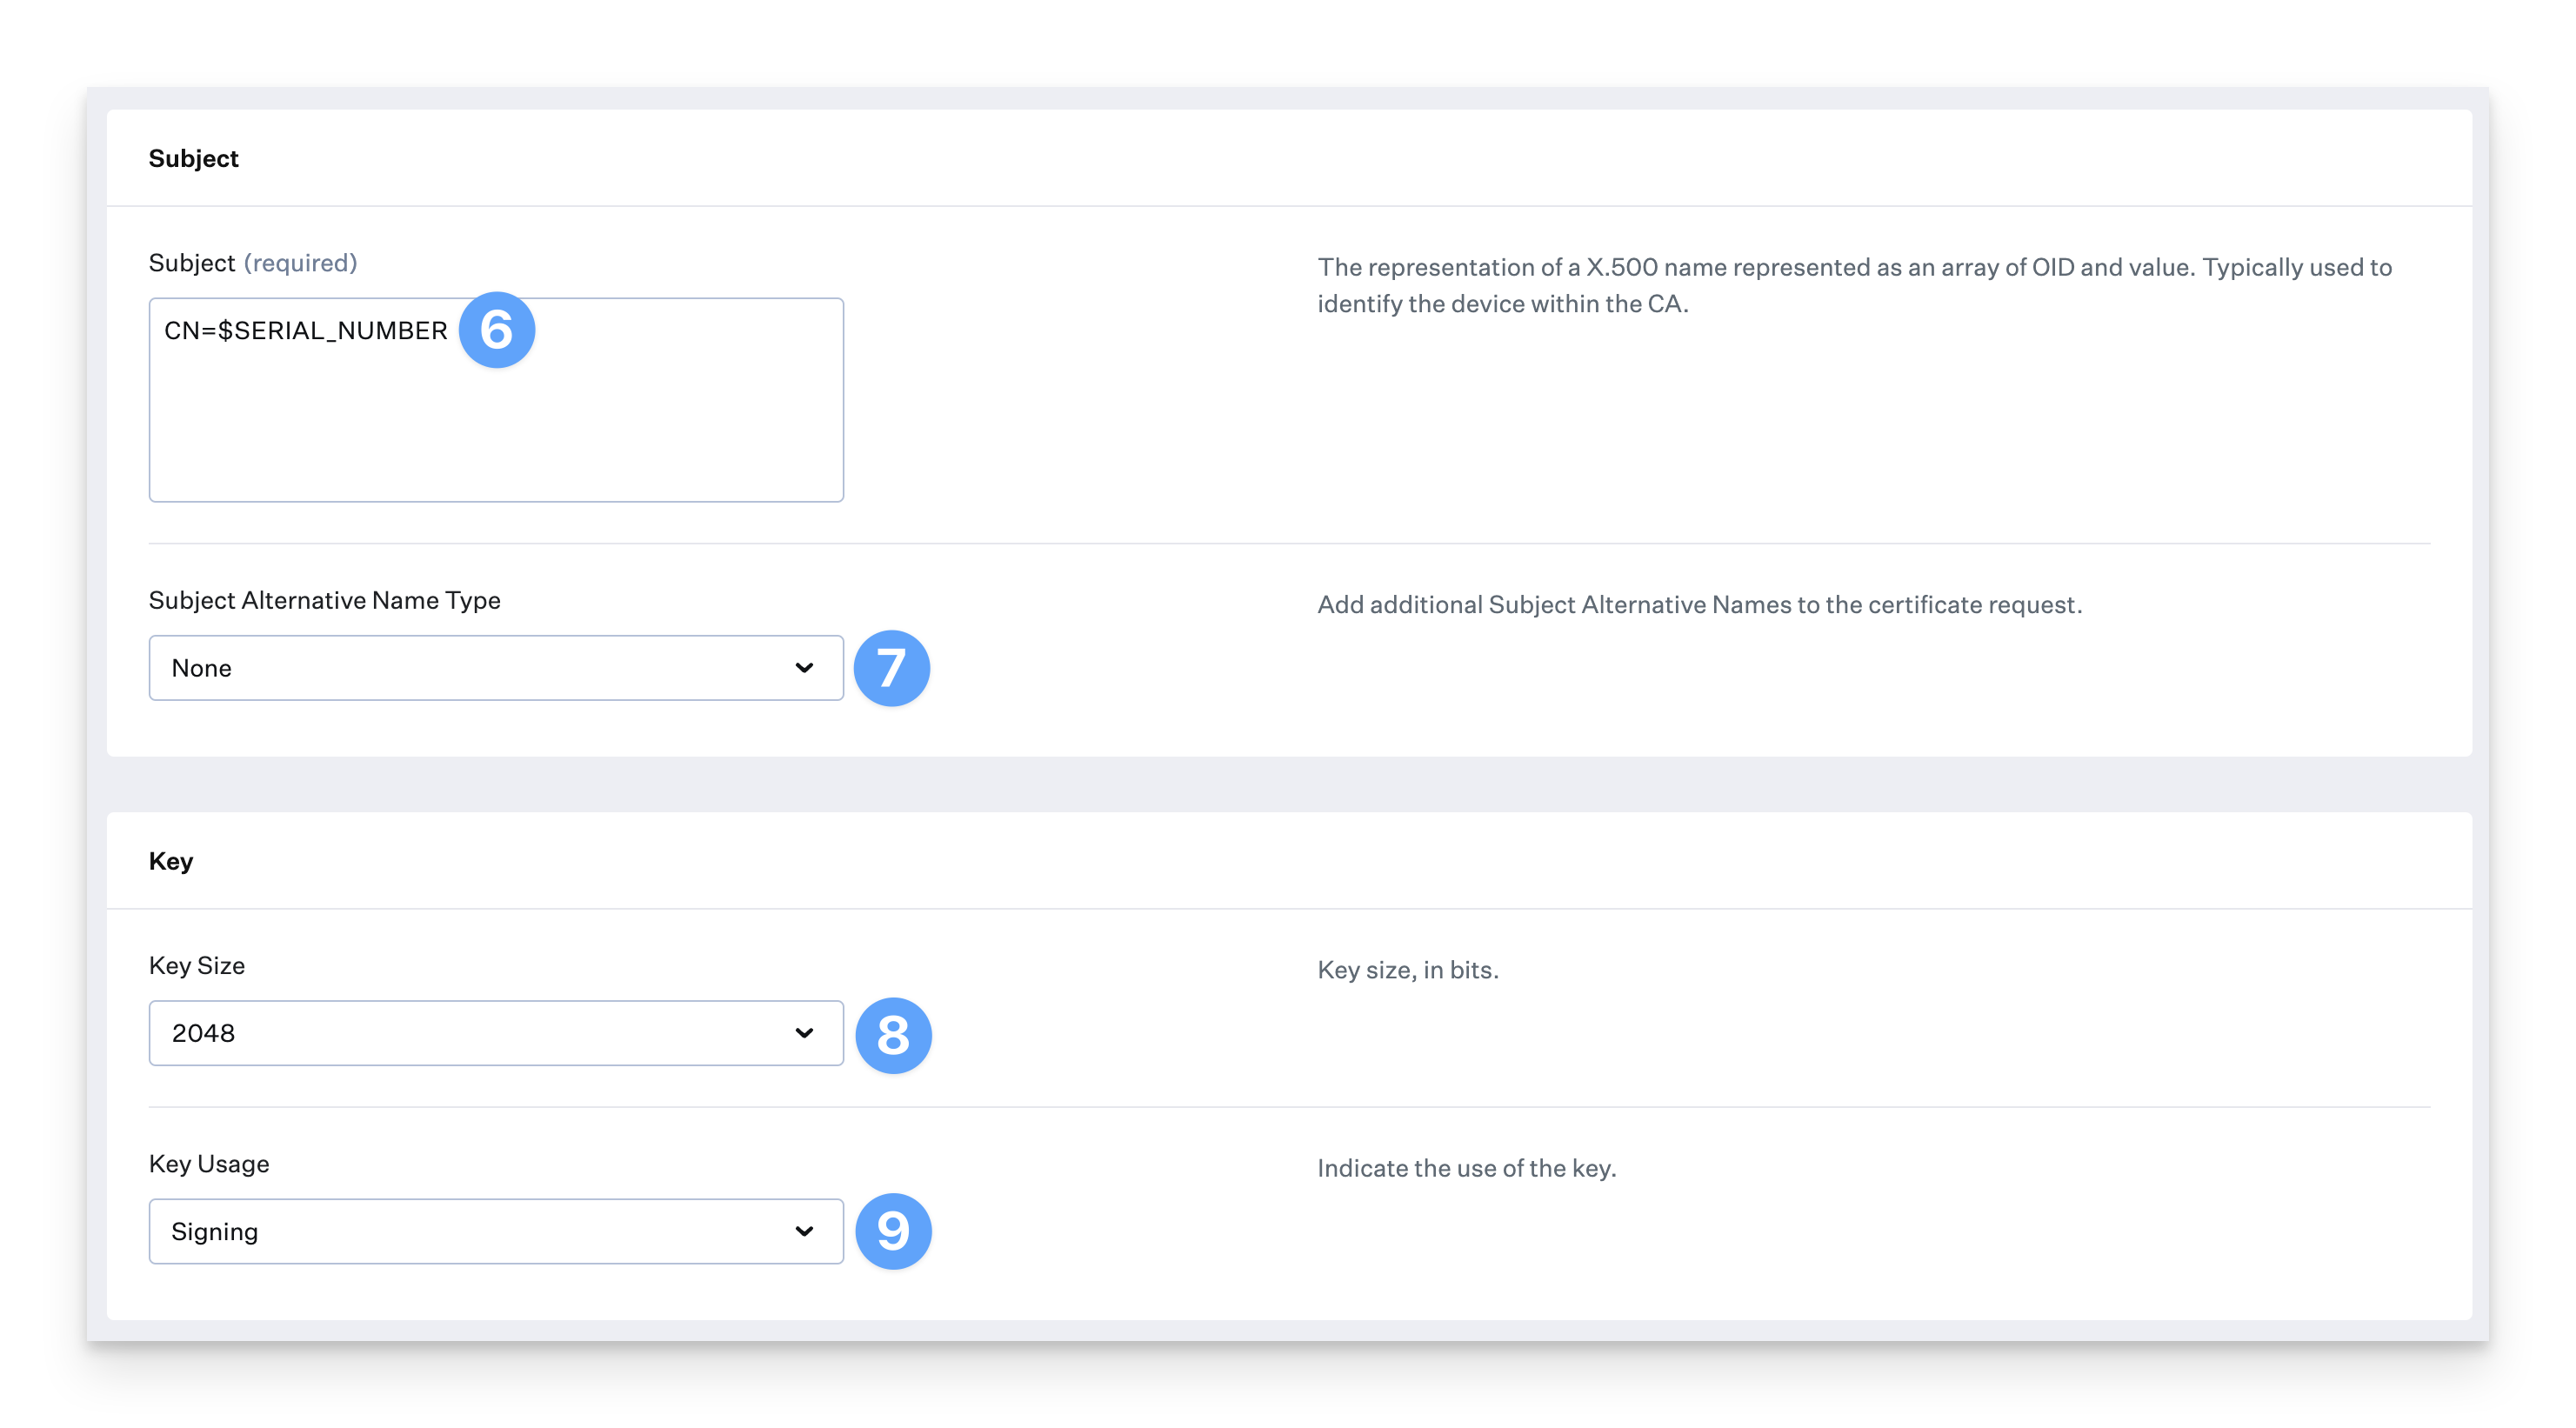
6. In the **Subject** field, enter CN=$SERIAL_NUMBER.
1. Upon saving the SCEP Library Item, Kandji will append the PROFILE_UUID to the end of the CN used.
7. Ensure that **Subject Alternative Name** Type is set to **None**.
8. For **Key Size**, select 2048.
9. For **Key Usage**, select Signing.
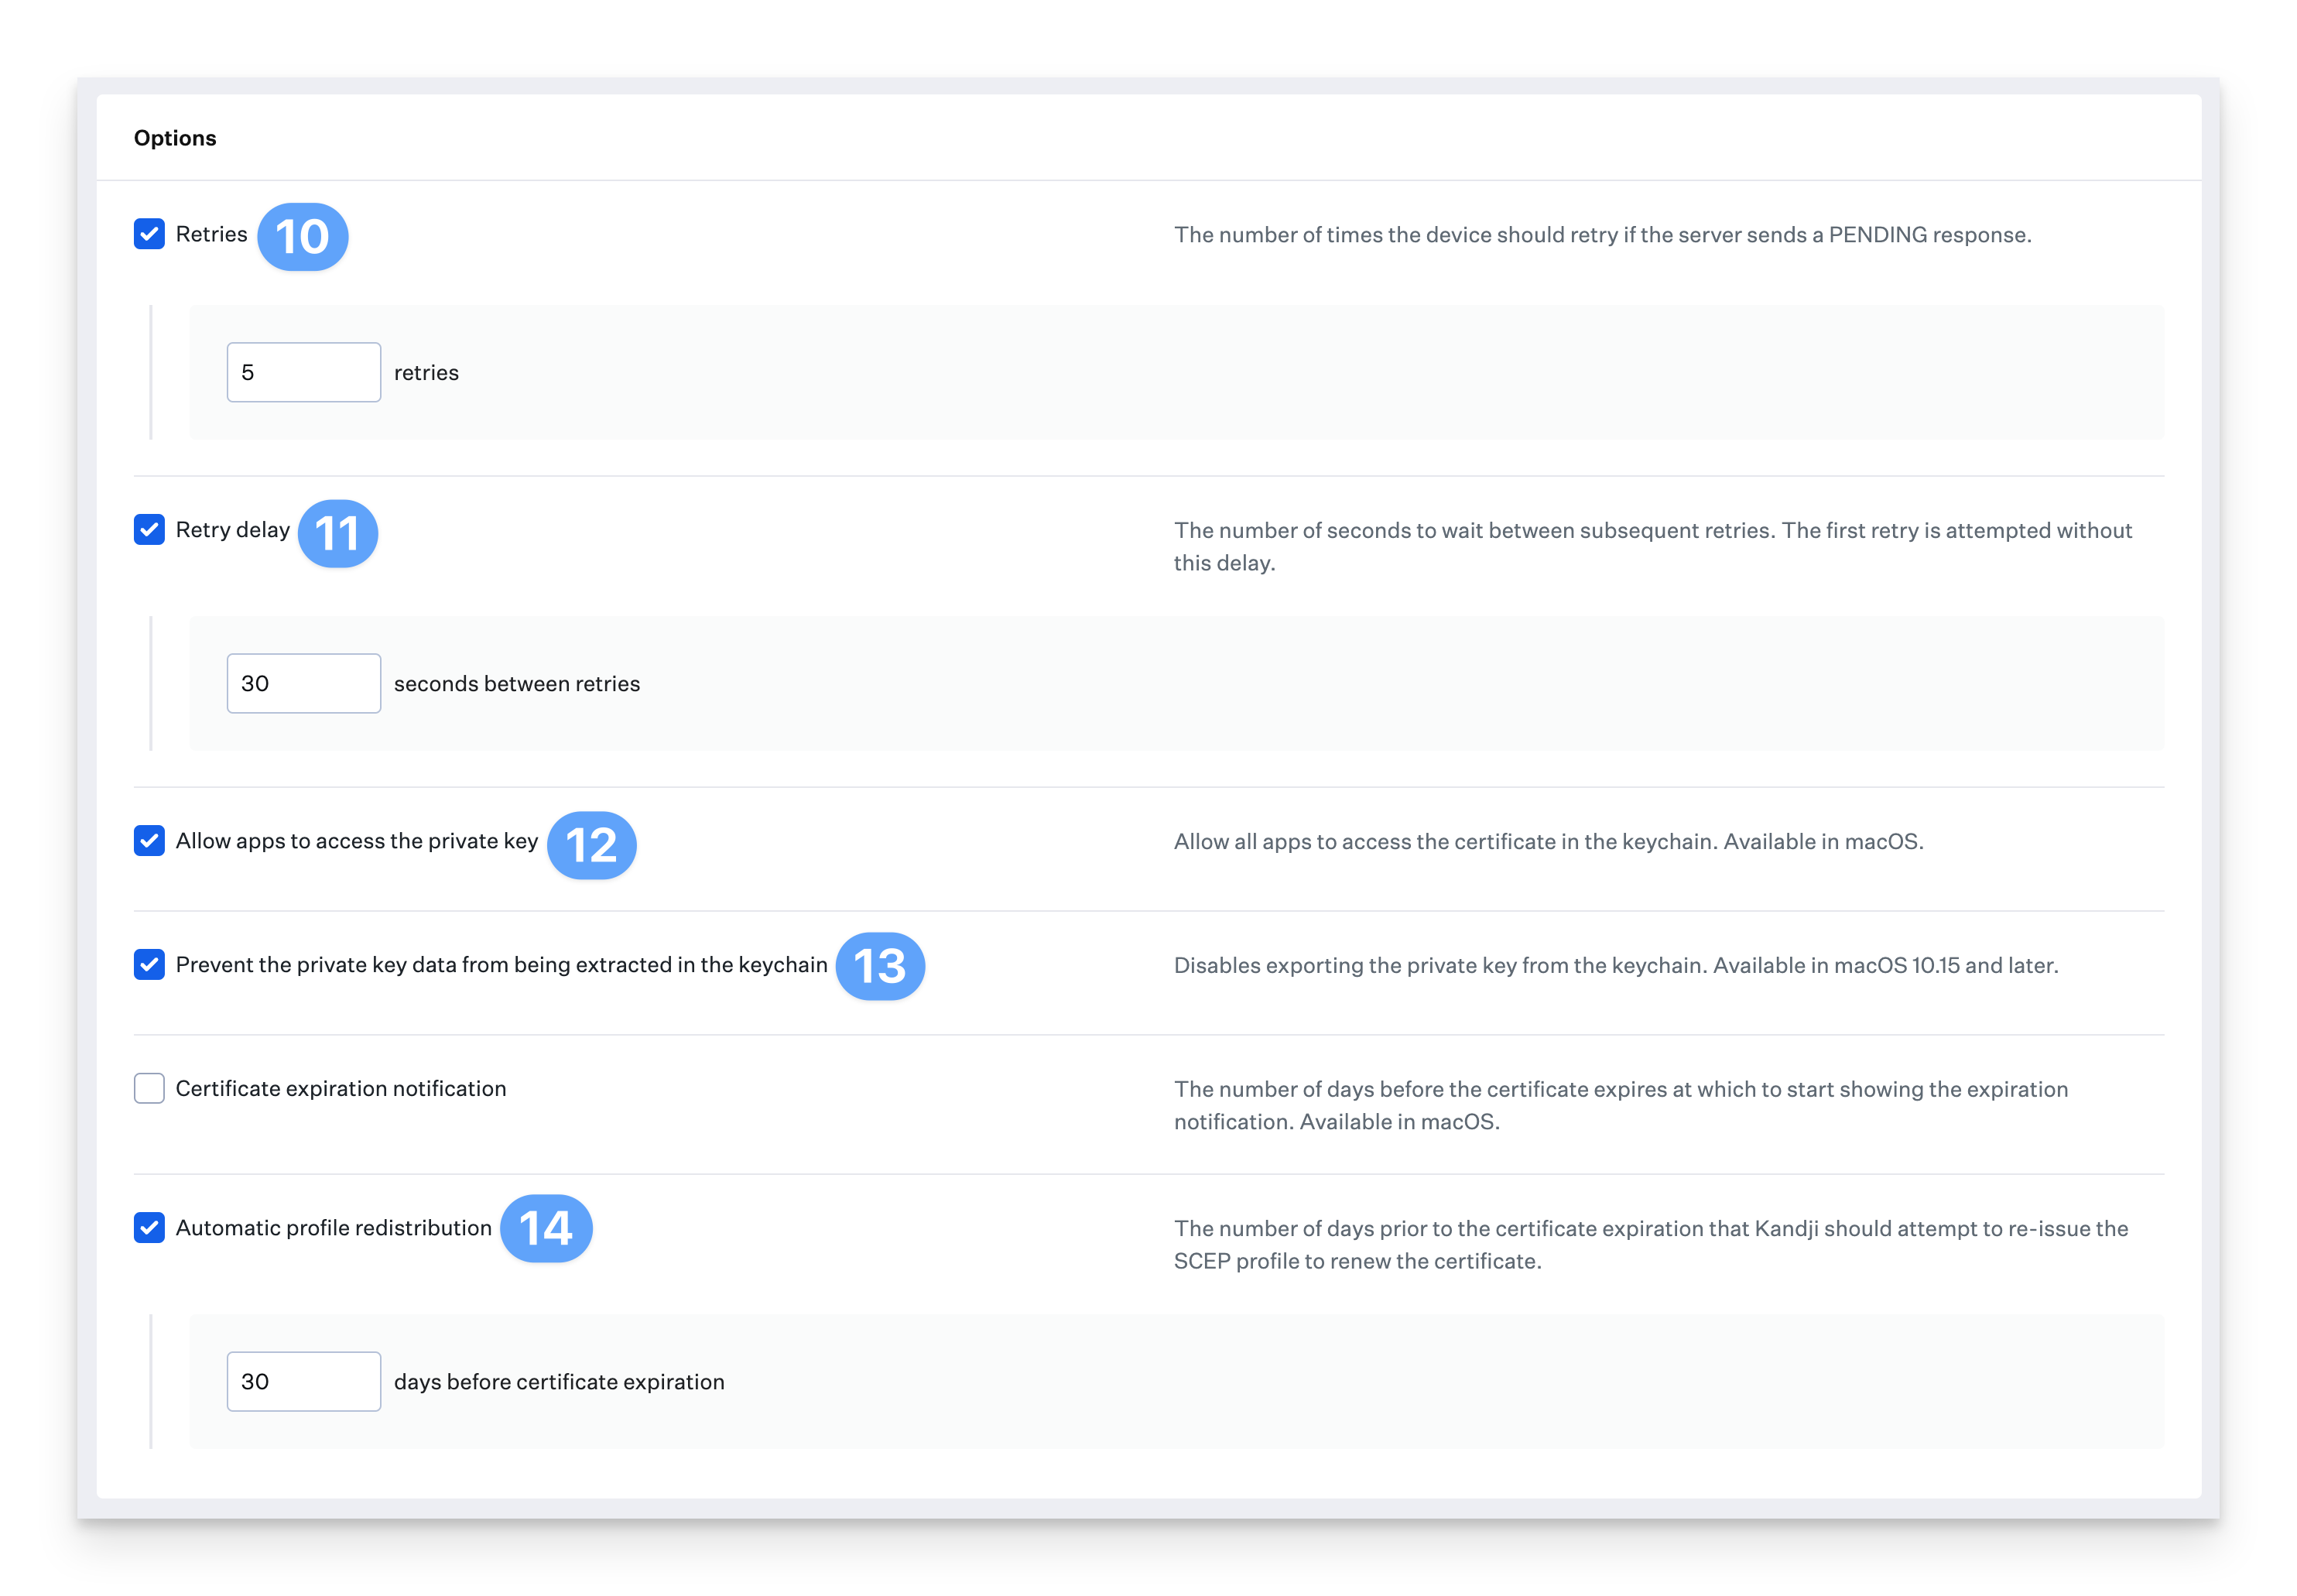
10. Select **Retries** and enter 5 for the number of retries. This number can be adjusted to a value that's appropriate for your environment.
11. Select **Retry delay** and enter 30 for the number of seconds. This number can be adjusted to a value that's appropriate for your environment.
12. Select **Allow apps to access the private key**.
13. Select **Prevent the private key date from being extracted in the keychain**.
14. Select **Automatic profile redistribution** and enter 30 for the days before the certificate expires. This number can be adjusted to a value that's appropriate for your environment.
15. Click Save.
For more information about the Kandji SCEP Library Item, please refer to the [SCEP Profile](/v1/docs/scep-profile) support article.
### Configure for macOS 13+
All of the settings in section apply for all versions of macOS unless otherwise noted. You need to configure separate instances of Okta Device Access for users on macOS 13 and macOS 14+.
### Create and configure the Desktop Password Sync app integration in Okta
1. In the Okta Admin Console, go to **Applications** > **Applications Catalog**.
2. Search for **Desktop Password Sync** and select the app.

3. Click **Add Integration**. If you get an error message saying This feature isn’t enabled, contact your Okta account representative.

4. Open Desktop Password Sync from your **Applications** list to configure it.
5. On the **General** tab, you can edit the application label or use the default label.
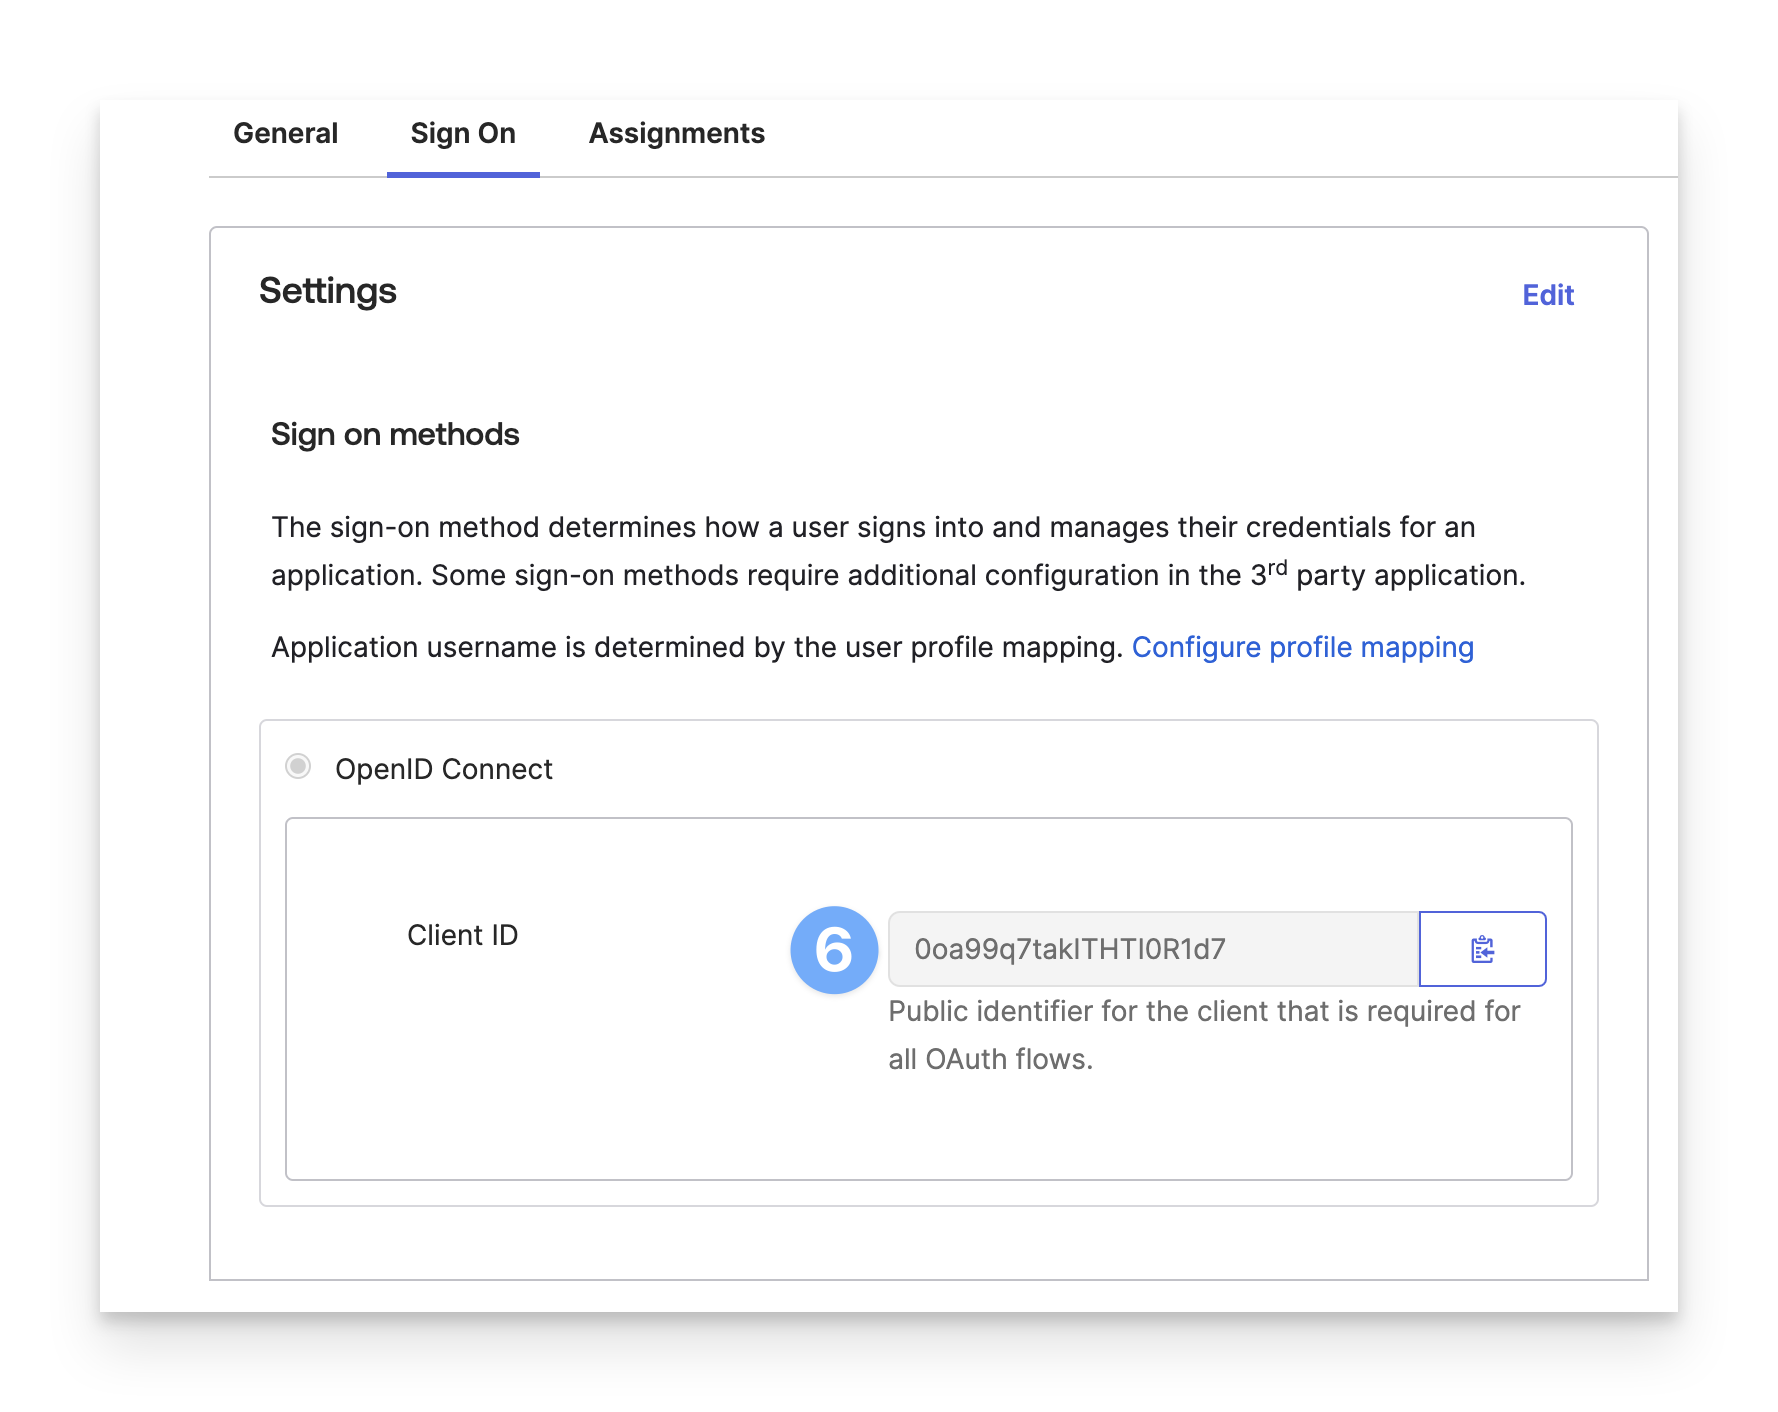
6. On the **Sign on** tab, take note of the Client ID. You will need this when creating the Single Sign-On profile.
7. Assign the app to individual users or groups on the **Assignments** tab. Users must be assigned the app to use Desktop Password Sync.
8. Click **Save**.
### Edit the mobileconfig template files
Three mobileconfig files are needed to enable Desktop Password Sync: two Platform SSO configuration profile and an Okta Verify configuration profile. When supporting macOS 13 and macOS 14+, you will need to deploy two of the Okta Verify configuration profiles. Follow the below steps to edit the provided templates and add them as Custom Profile Library Items in Kandji. You must edit them using a plain text editor such as Visual Studio Code, Sublime Text, BBEdit, etc.
> [!NOTE]
> If you will not be supporting macOS 13 devices in your fleet, you can skip deploying the Okta_PSSO_Configuration_Template_macOS13.mobileconfig Profile.
1. Download the Okta_PSSO_Configuration_Template_macOS13.mobileconfig file from the Kandji support GitHub repository ([GitHub Link](https://github.com/kandji-inc/support/blob/main/Configuration%20Profiles/Okta_PSSO_Configuration_Template_macOS13.mobileconfig)).
2. Download the Okta_PSSO_Configuration_Template_macOS14.mobileconfig file from the Kandji support GitHub repository ([GitHub Link](https://github.com/kandji-inc/support/blob/main/Configuration%20Profiles/Okta_PSSO_Configuration_Template_macOS14.mobileconfig)).
3. Download the Okta_Verify_Configuration_Template.mobileconfig file from the Kandji support GitHub repository ([GitHub Link](https://github.com/kandji-inc/support/blob/main/Configuration%20Profiles/Okta_Verify_Configuration_Template.mobileconfig)).
#### Okta PSSO Configuration Profile for macOS 13
1. Open the **Okta_PSSO_Configuration_Template_macOS13.mobileconfig** file in your text editor.
2. Update the **AssociatedDomains** section of the Associated Domains payload, replacing the example domain with your own Okta tenant address.
- Example: authsrv:accuhive.okta.com
```xml
AssociatedDomains
authsrv:accuhive.okta.com
```
3. Update the **URLs** section of the Extensible SSO payload and replace the example domain with your Okta tenant information. Leave the rest of the URL as is.
- Example: accuhive.okta.com
```xml
URLs
https://accuhive.okta.com/device-access/api/v1/nonce
https://accuhive.okta.com/oauth2/v1/token
```
4. Save the mobileconfig file.
#### Okta PSSO Configuration Profile for macOS 14+
1. Open the **Okta_PSSO_Configuration_Template_macOS14.mobileconfig** file in your text editor.
2. Update the **AssociatedDomains** section of the Associated Domains auth-service-extension payload, replacing the example domain with your own Okta tenant address.
- Example: authsrv:accuhive.okta.com
```xml
ApplicationIdentifier
B7F62B65BN.com.okta.mobile.auth-service-extension
AssociatedDomains
authsrv:accuhive.okta.com
```
3. Update the **AssociatedDomains** section of the Associated Domains payload, replacing the example domain with your own Okta tenant address.
- Example: authsrv:accuhive.okta.com
```xml
ApplicationIdentifier
B7F62B65BN.com.okta.mobile
AssociatedDomains
authsrv:accuhive.okta.com
```
4. Update the **URLs** section of the Extensible SSO payload and replace the example domain with your Okta tenant information. Leave the rest of the URL as is.
- Example: accuhive.okta.com
```xml
URLs
https://accuhive.okta.com/device-access/api/v1/nonce
https://accuhive.okta.com/oauth2/v1/token
```
5. Save the mobileconfig file.
#### Okta Verify Configuration Profile
1. Open the **Okta_Verify_Configuration_Template.mobileconfig** file in your text editor.
2. Update the **OktaVerify.OrgUrl** section of the com.okta.mobile payload with your Okta tenant URL.
1. Example: https://accuhive.okta.com
```xml
OktaVerify.OrgUrl
https://accuhive.okta.com
```
3. Update the **OktaVerify.PasswordSyncClientID** section of the com.okta.mobile payload with the Client ID of your Desktop Password Sync app that you recorded earlier.
```xml
OktaVerify.PasswordSyncClientID
YOUR_CLIENT_ID
```
4. Update the **OktaVerify.OrgUrl** section of the com.okta.mobile.auth-service-extension payload with your Okta tenant URL.
```xml
OktaVerify.OrgUrl
https://accuhive.okta.com
```
5. Update the **OktaVerify.PasswordSyncClientID** section of the com.okta.mobile.auth-service-extension payload with the Client ID of your Desktop Password Sync app that you recorded earlier.
```xml
OktaVerify.PasswordSyncClientID
YOUR_CLIENT_ID
```
6. Update the the **PlatformSSO.ProtocolVersion** section of the com.okta.mobile.auth-service-extension payload to the appropriate version for your org.
1. For macOS 13 Ventura, set to 1.0
2. For macOS 14 Sonoma or later, set to 2.0
```xml
PlatformSSO.ProtocolVersion
2.0
```
3. If you will be supporting macOS 13 and macOS 14+, you will need to save multiple versions of the **Okta_Verify_Configuration_Template.mobileconfig** file, each with the appropriate **PlatformSSO.ProtocolVersion** setting.
7. Save the mobileconfig file(s).
### Create the Custom Profiles Library Items in Kandji
To add this Library Item to your Kandji Library, follow the steps outlined in the [Library Overview](/kb/library-overview) article.
1. Provide a name for the Library Item.
2. Assign it to your desired [Blueprints](/v1/docs/getting-started-with-assignment-maps).
3. Upload the modified “Okta_PSSO_Configuration_Template_macOS13.mobileconfig” file.
4. Click Save.
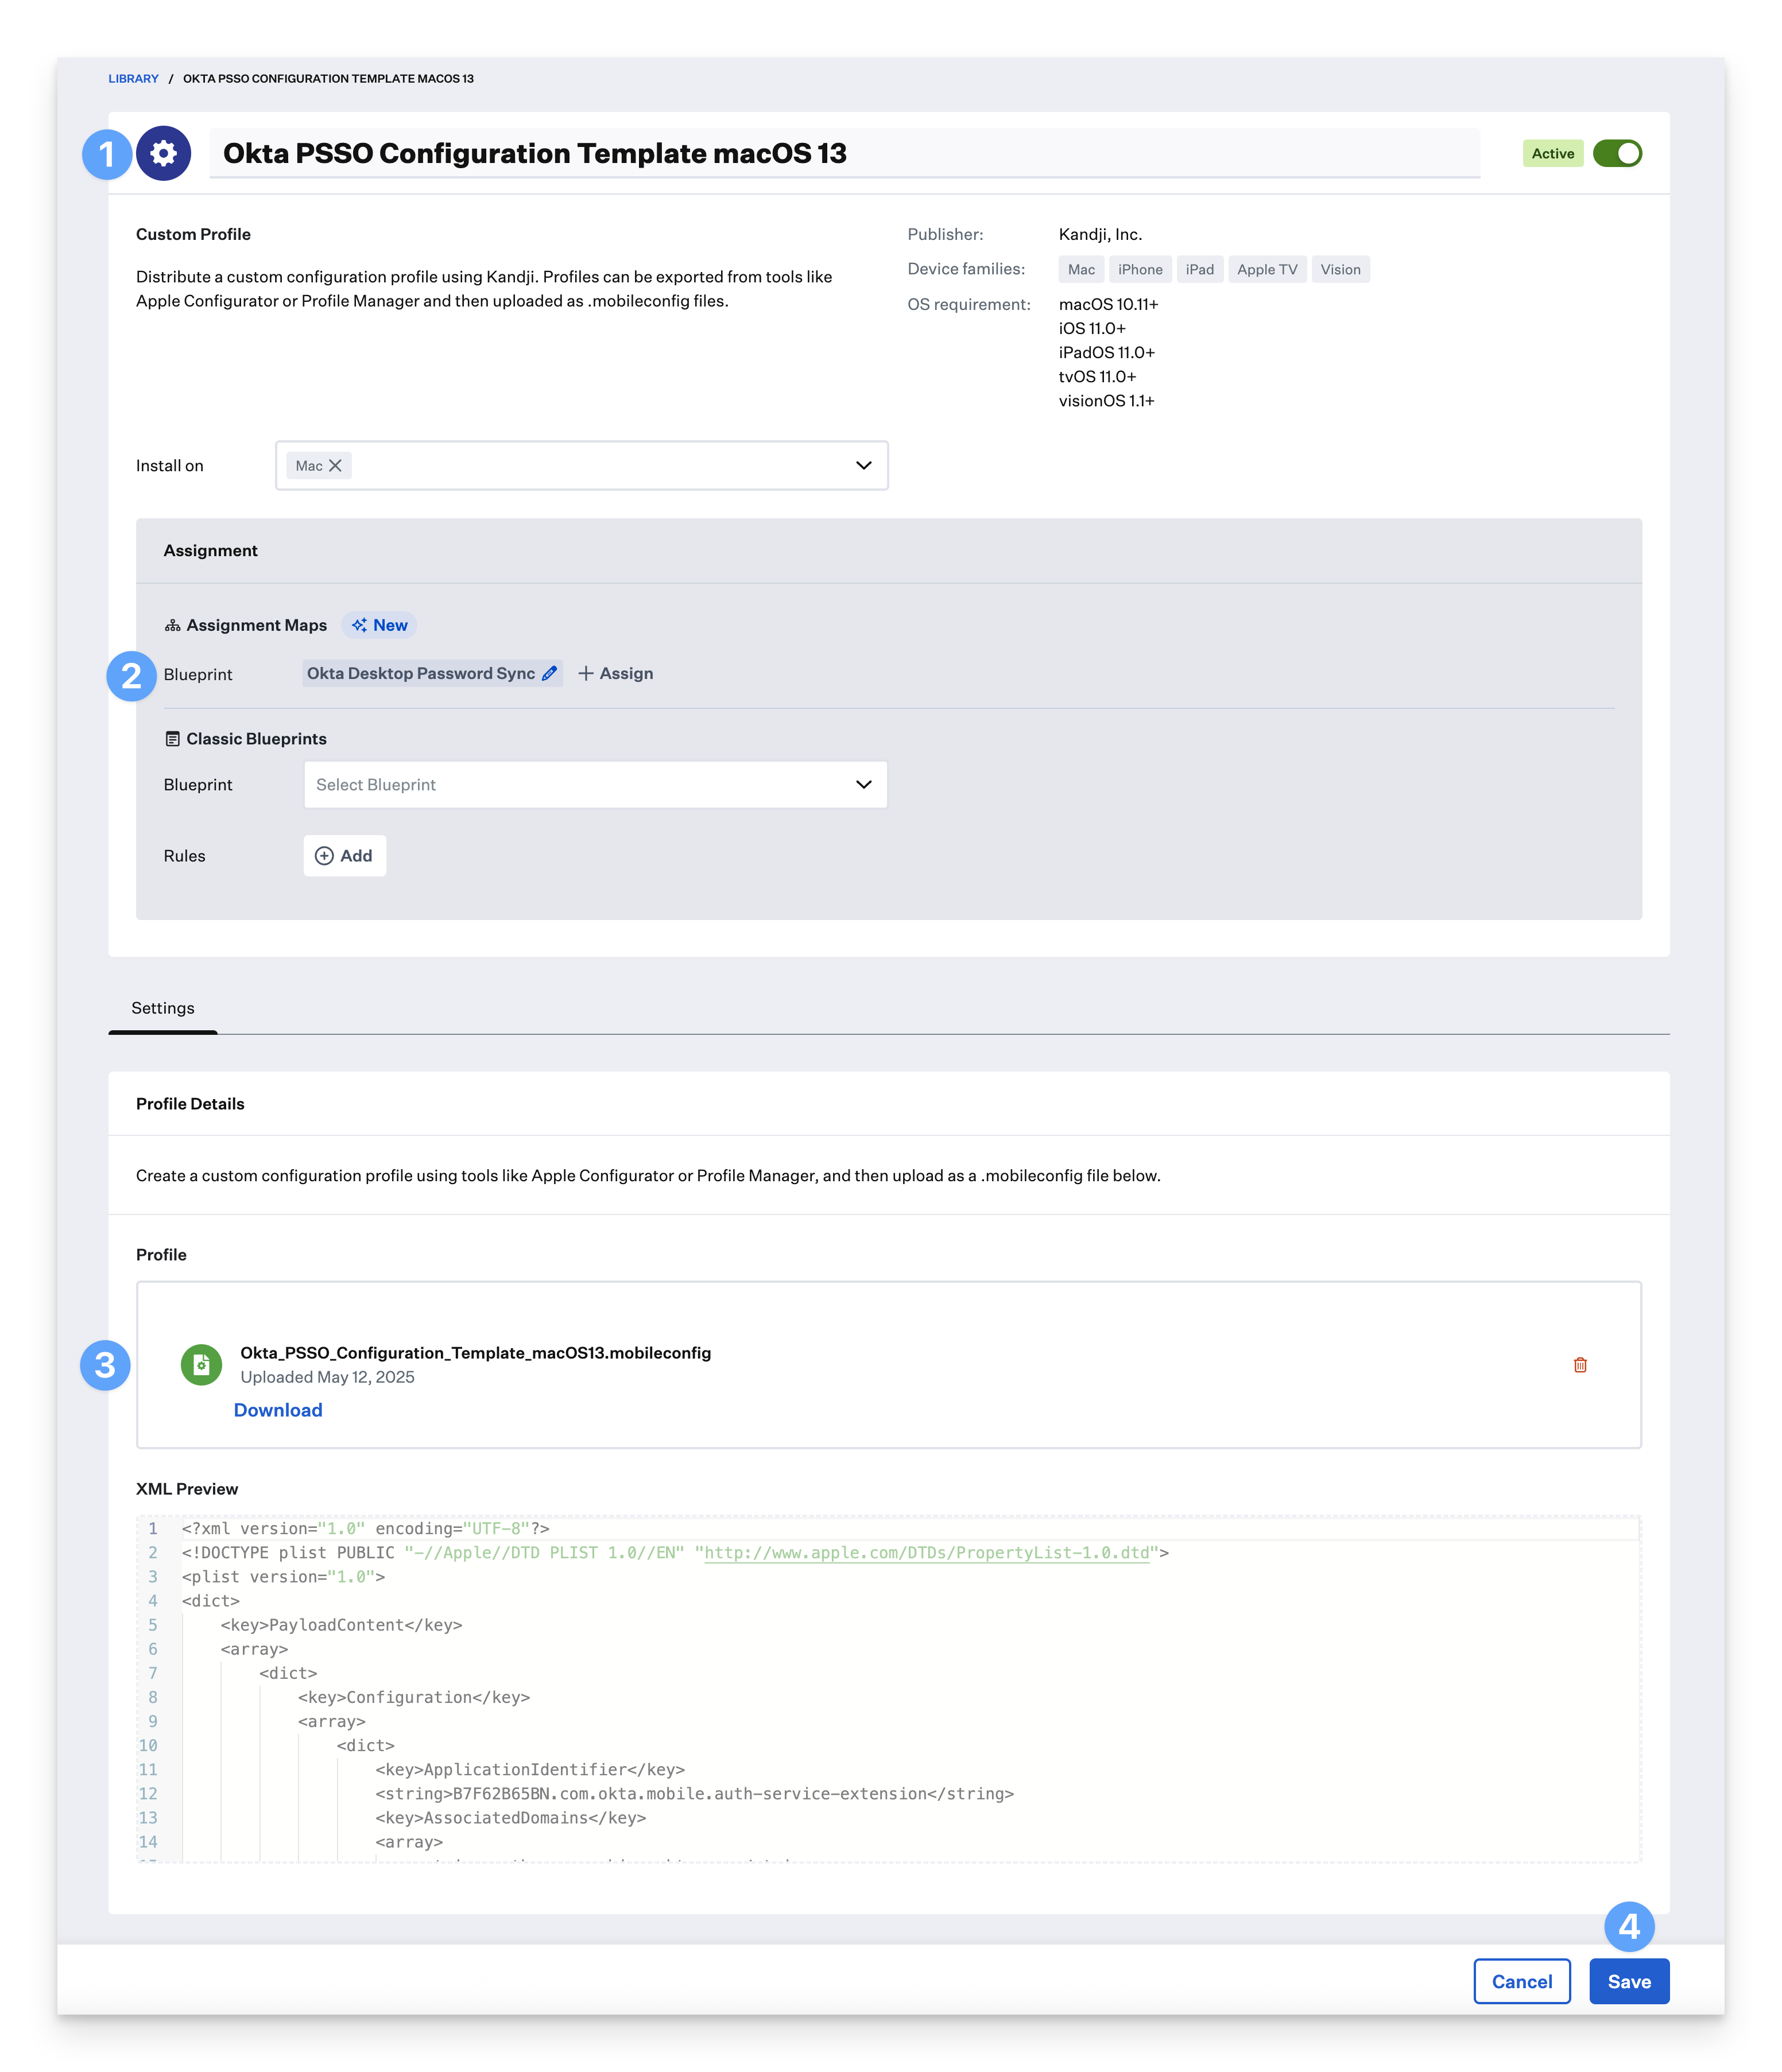
5. Repeat the previous steps in this section for the “Okta_PSSO_Configuration_Template_macOS14.mobileconfig” and for all “Okta_Verify_Configuration_Template.mobileconfig” files.
6. Ensure the Okta Verify app is assigned to the same Blueprint(s) as the Custom Profile Library Items created earlier.
7. Follow the steps in the Deploying Profiles with Assignment Maps section so that Profiles are only deployed to compatible devices.
8. Once the profiles and Okta Verify app are distributed to your Mac computers, users will be prompted to register and synchronize their Okta password.
### Deploying Profiles with Assignment Maps
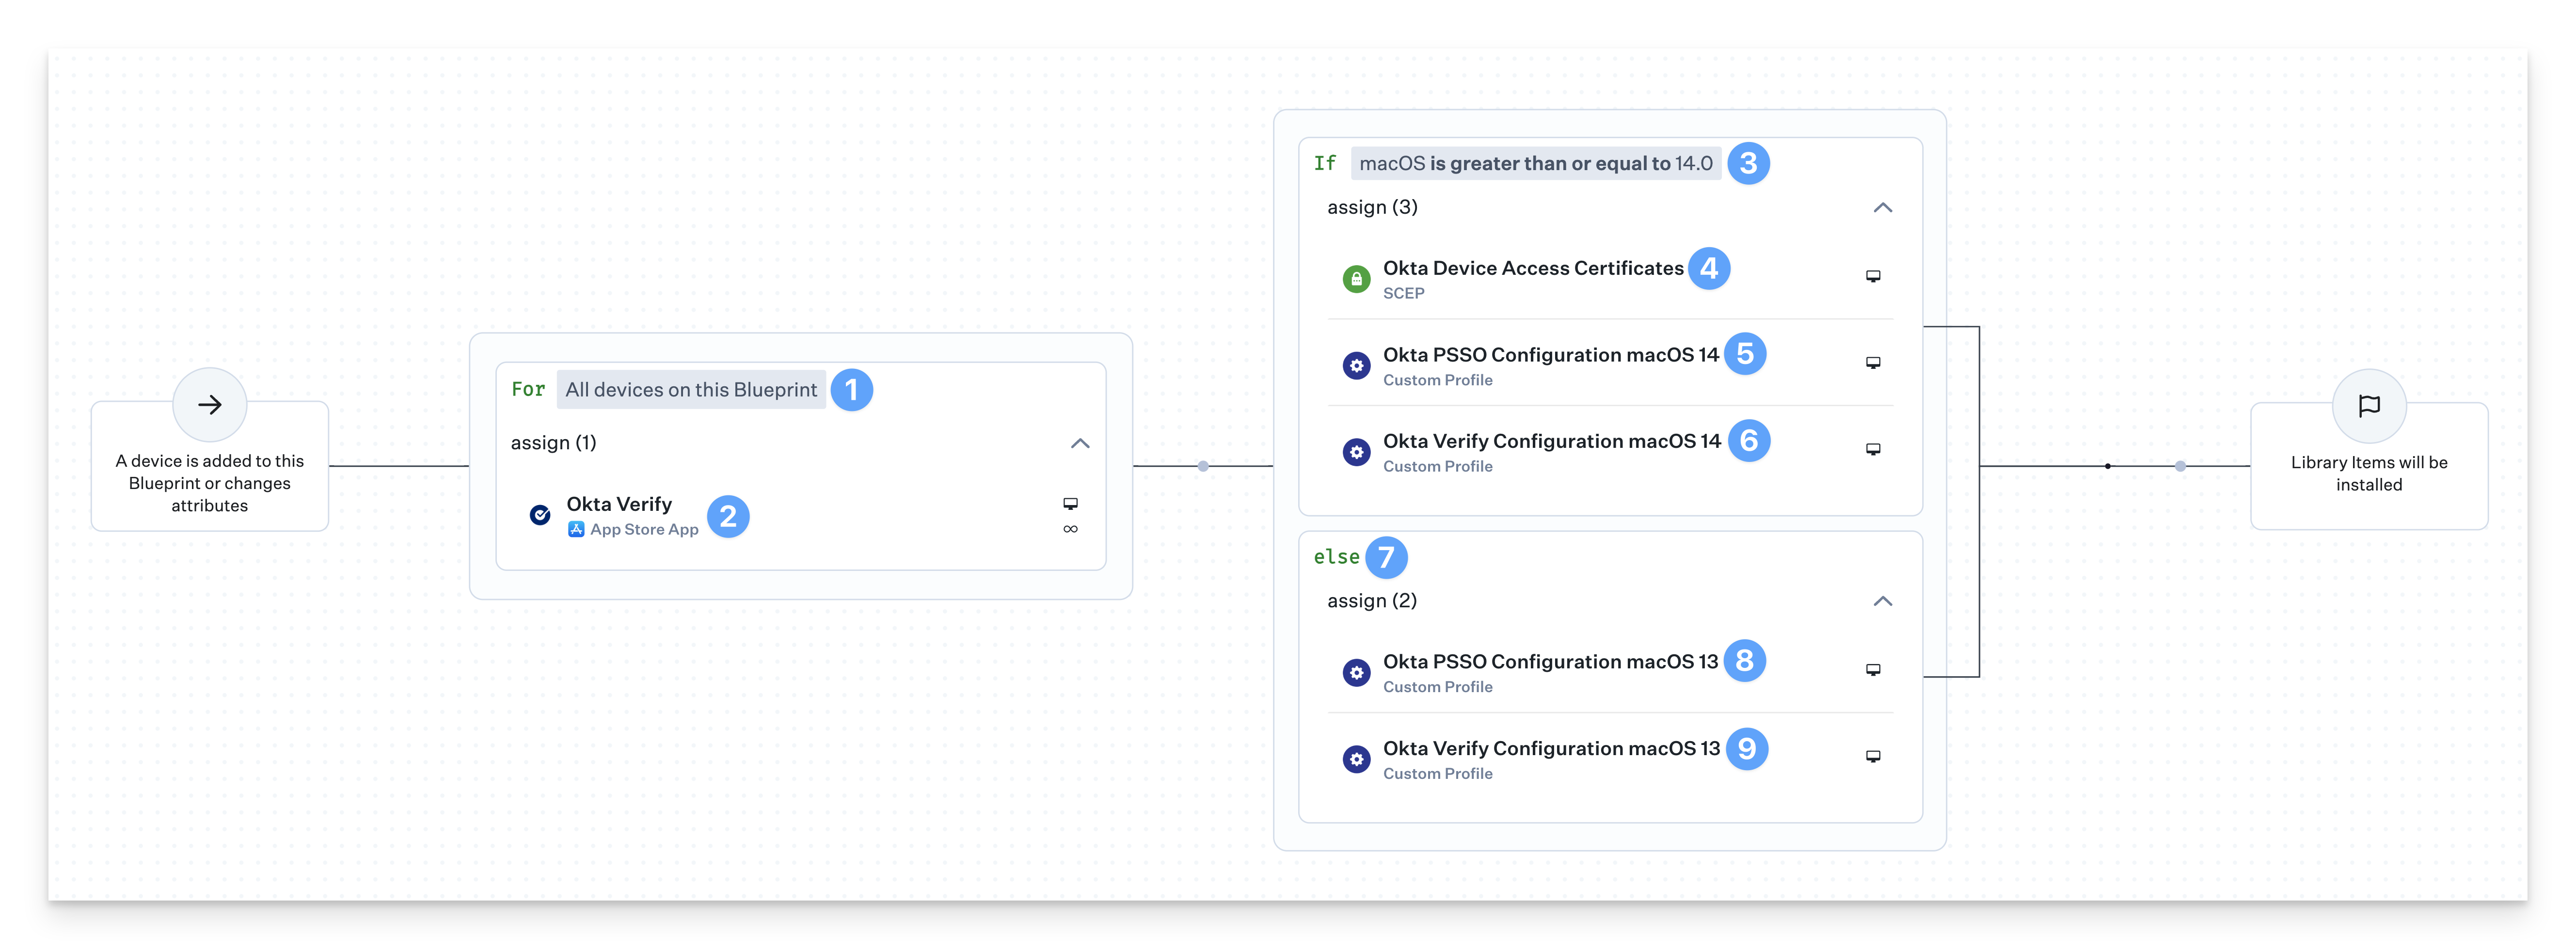
There are up to four Crowdstrike Custom Profiles that need conditional logic to ensure they are deployed to the correct devices. An Assignment Map provides an easy solution for all of your devices in one convenient view.
Please review our [Creating a Blueprint](/v1/docs/getting-started-with-assignment-maps) and [Using Conditional Logic in Assignment Maps](/v1/docs/advanced-assignment-maps-configuration) articles.
1. Start with the **For All devices on this Blueprint** conditional block.
2. Assign the **Okta Verify** App Store App to the block.
3. Set the top of the conditional block to **If** **macOS is greater than or equal to 14.0**.
4. Assign the **Okta Device Access Certificates SCEP** Library Item to the conditional block.
5. Assign the **Okta PSSO Configuration macOS 14** Custom Profile to the conditional block.
6. Assign the **Okta Verify Configuration macOS 14** Custom Profile to the conditional block.
7. Continue in the **else** section of the conditional block.
8. Assign the **Okta PSSO Configuration macOS 13** Custom Profile to the conditional block.
9. Assign the **Okta Verify Configuration macOS 13** Custom Profile to the conditional block.
### User Experience and Next Steps
> [!NOTE]
> With Platform SSO, by design from Apple, in Users & Groups settings, in the Password field, the Change button is not available.
Once the Okta Desktop Password configuration is complete, you can have your users follow the steps in the [User Experience with Okta Desktop Password Sync](/docs/user-experience-with-okta-desktop-password-sync) article to get them registered.